Avint, LLC

Solutions

Practitioners, not headcount

Avint people engineer, defend and authorize federal systems every day. These are the six capabilities they deliver, and the technology they build.

What we do

Mission-Critical Cybersecurity Solutions

We safeguard enterprise and public-sector environments through unified engineering, continuous operations, modern risk governance, and applied AI automation. Spanning the entire system lifecycle, our services help organizations build resilient architectures, counter active threats, and sustain rapid Authorizations to Operate.

Cybersecurity Engineering & Architecture

Engineer security into the mission

Security architecture, Zero Trust, cloud security, secure design, threat modeling, system hardening, and cybersecurity engineering across complex enterprise environments.

Core focus
Zero Trust implementations (NIST SP 800-207, CISA ZTMM), hybrid and multi-cloud posture management, DevSecOps pipeline security, and system hardening via DISA STIGs and CIS Benchmarks.
Key impact
Elimination of architectural misconfigurations, significantly reduced attack surfaces, and systems engineered for seamless, ongoing compliance.

Delivered by

Security architects and cybersecurity engineers
Threat, Vulnerability & Exposure Management

Turn threat intelligence into remediation priorities

Threat intelligence, vulnerability management, attack-path analysis, penetration testing, cyber hunt, and risk-based remediation informed by real-world exploitation.

Core focus
Predictive vulnerability prioritization (CISA KEV, EPSS, MITRE ATT&CK), red teaming and adversary emulation, threat hunting, and software supply chain security (SBOM).
Key impact
Accelerated risk reduction, strategic allocation of engineering resources, and defensible, data-backed remediation roadmaps.

Delivered by

Threat analysts, cyber hunt teams and penetration testers

equipped with Avint Threat Intelligence Platform

Security Operations & Incident Response

Defend systems continuously

Cyber defense, detection engineering, incident response, security operations, continuous monitoring, and operational support for high-value environments.

Core focus
Turnkey SOC staffing, custom detection engineering, SIEM and SOAR optimization, digital forensics, and structured incident response aligned with NIST SP 800-61.
Key impact
Drastically reduced adversary dwell time, faster incident containment, and predictable, fully audited response procedures.

Delivered by

Cyber defenders, detection engineers and incident responders

equipped with Threat Landscape

AI-Enabled Cybersecurity

Apply AI where it changes the mission

Agentic AI, cybersecurity automation, AI-assisted assessment, secure AI engineering, and purpose-built AI/ML solutions that reduce manual security workload and accelerate decisions.

Core focus
Autonomous security workflows, AI-assisted compliance analysis, automated threat correlation, and AI security governance aligned with the NIST AI Risk Management Framework.
Key impact
Faster alert triage, reduced analyst fatigue, and secure model deployment across both cloud and air-gapped networks.

Delivered by

Data scientists and AI engineers

equipped with Ask Alloy

Cyber Risk & Authorization

Make risk visible, defensible, and actionable

RMF modernization, security control assessment, continuous authorization, cyber risk analysis, C-SCRM, and executive-level risk visibility.

Core focus
Modernized NIST RMF (SP 800-37 and 800-53) and FedRAMP alignment, continuous ATO enablement, supply chain risk management (C-SCRM, NIST SP 800-161), and GRC automation.
Key impact
Streamlined authorization timelines, automated compliance evidence collection, and transparent risk reporting for leadership.

Delivered by

Security control assessors and cyber risk analysts

equipped with ATO Workflow

ISSO as a Service

Operate and accelerate the authorization lifecycle

Embedded ISSO and ISSE expertise across RMF, ATO, continuous monitoring, POA&M management, control evidence, and ongoing authorization.

Core focus
Comprehensive System Security Plan maintenance, end-to-end ATO package assembly, POA&M remediation, and security impact evaluations for ongoing engineering changes.
Key impact
Uninterrupted compliance, audit-ready authorization packages, and proactive resolution of security findings.

Delivered by

Embedded ISSOs and ISSEs

equipped with Avint ISSO Advisory Assistant

The same operational experience that drives these missions shapes AlloyGRC, turning lessons learned in the field into automation, intelligence, and product capabilities.

Avint AI Lab

Where Mission Meets Machine Intelligence

Avint invests in applied AI and machine learning to solve cybersecurity challenges our practitioners encounter every day. Our technology helps teams understand risk faster, prioritize what matters, reduce manual effort, and make better-informed security decisions.

Avint's AI Lab is the engine of our Technology Innovation Group, a dedicated environment where we design, build, and prove AI solutions for the federal mission. We don't just evaluate emerging technology. We build it, test it against real federal requirements, and deliver it ready for operational use.

Our investment reflects a simple conviction: federal agencies need AI they can trust, govern, and deploy securely. We build to that standard.

Our Technologies

  • AI-powered GRC platform

    AlloyGRC

    AI-enabled cyber risk, authorization, and continuous compliance.

    See AlloyGRC
  • Vulnerability intelligence

    AREA

    Threat-informed vulnerability intelligence and prioritization.

    AREA on alloygrc.com
  • AI practitioner assistant

    AVISSAA

    AI-powered assistance for cybersecurity practitioners.

    AVISSAA on alloygrc.com

Avint AI Lab

What We Build

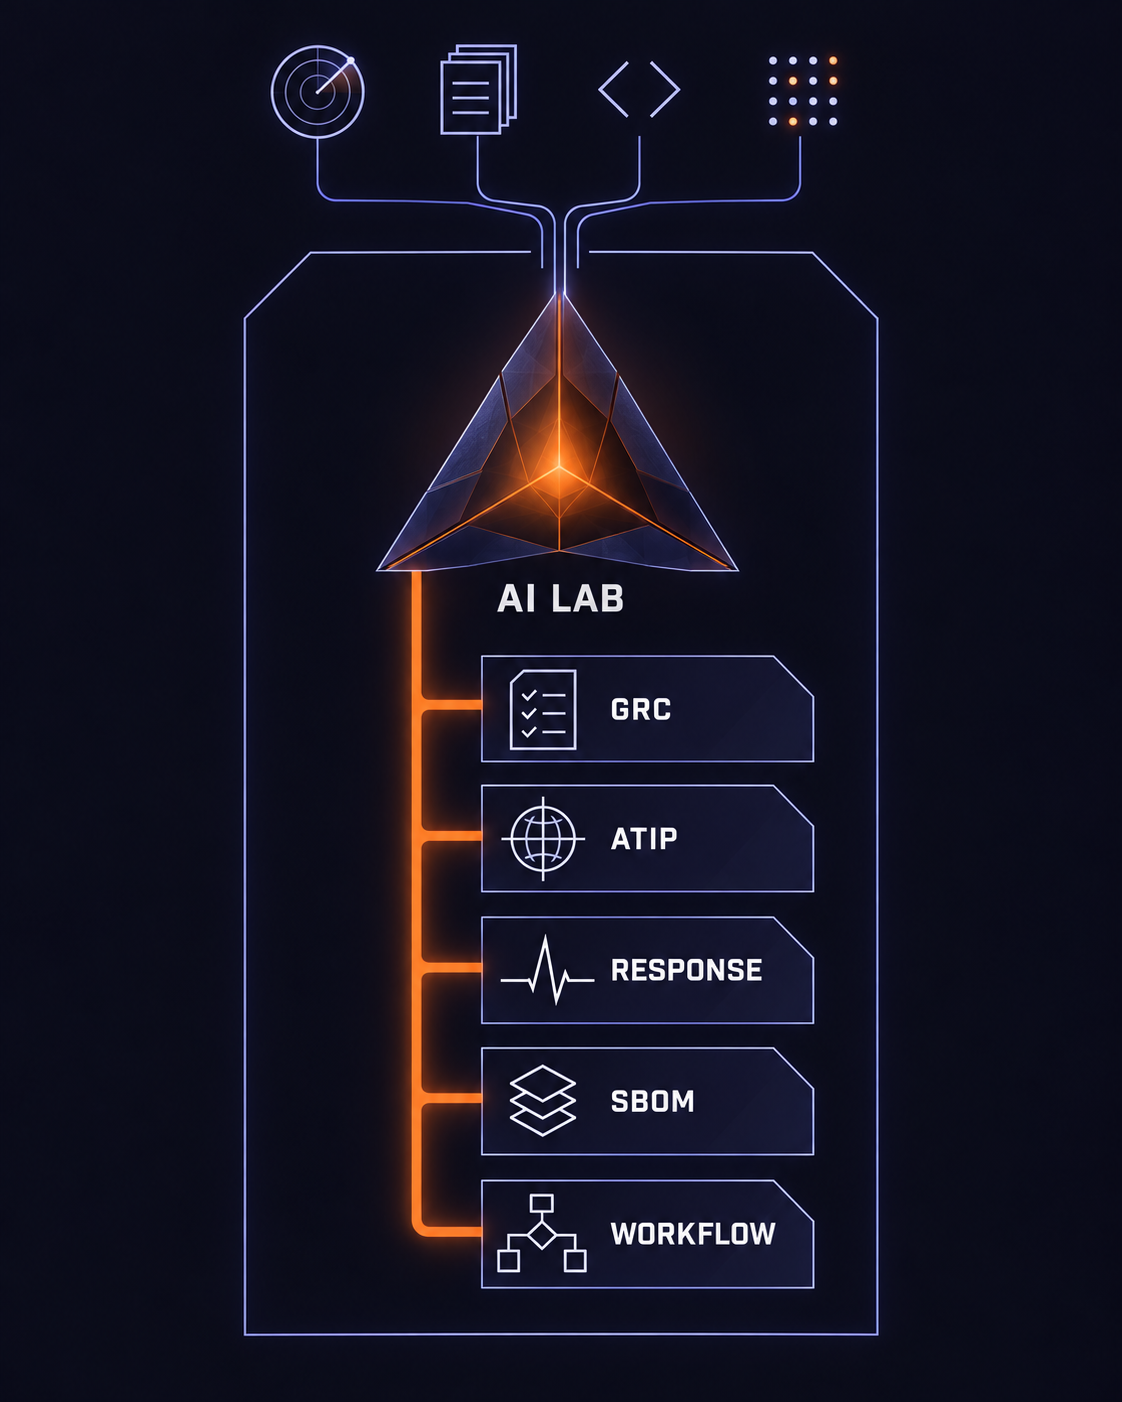
Diagram: threat data, evidence, code and alerts pass into a secure boundary and feed the Avint AI Lab, which delivers five capabilities: GRC, ATIP threat intelligence, incident response, SBOM software assurance and authorization workflow.
  • AI-Driven Governance, Risk & Compliance

    AlloyGRC brings intelligent automation to the full compliance lifecycle, from control assessment and policy development to evidence analysis and continuous Authorization to Operate (cATO). What once took weeks of manual review now moves at the speed of the mission.

  • Threat Intelligence at Scale

    The Avint Threat Intelligence Platform (ATIP) collects and correlates threat data and maps vulnerabilities to adversary tactics and techniques in the MITRE ATT&CK framework. Defenders get context, not just alerts.

  • Agentic Incident Response

    AI agents work alongside security operations teams to triage, investigate, and respond to incidents, reducing analyst fatigue and shortening time to containment.

  • Software Assurance

    Automated software composition analysis and SBOM generation help agencies find and fix weaknesses before adversaries do.

  • Workflow Automation for Authorization

    BPMN-based workflow tools model and execute ATO processes, bringing structure, repeatability, and auditability to one of the most resource-intensive activities in federal IT.

Our Approach

  • Secure by Design.

    Every solution is built with federal security requirements in mind from day one, not bolted on afterward.

  • Private and Sovereign AI.

    Our AI solutions operate within agency boundaries, keeping sensitive data where it belongs.

  • Practitioner-Led.

    Our lab is led by certified security and governance professionals who have lived the compliance and cyber challenges our clients face.

  • Mission-Proven.

    Solutions move from prototype to production because they are shaped by real federal use cases, not hypothetical ones.

Investing in the Next Generation

Through our partnership with George Mason University's Cyber Security Engineering program, the AI Lab sponsors capstone projects that give students hands-on experience solving real-world cybersecurity challenges.

Innovation That Delivers

At Avint, AI is not a buzzword. It is a disciplined practice of building secure, explainable, and mission-ready capabilities that help federal agencies protect what matters and operate with confidence.

The advantage

Why programs keep us

  • Mission-aligned strategy

    Security frameworks built around core organizational objectives, not checkbox compliance.

  • Deep regulatory mastery

    Proven execution across NIST, CISA, DISA, and FedRAMP requirements.

  • Unified lifecycle delivery

    Seamless integration across architecture, front-line operations, risk governance, and automation.

  • Pragmatic modernization

    Strategic use of AI and automated workflows where they deliver quantifiable reductions in workload and risk.

Careers

Join our team

At Avint, Avid Integrity and Empower Excellence aren't just values, they define how we work. We hire exceptional people, trust them to lead, and give them the space and support to do the best work of their careers.